

Identity, policy and evidenceacross every agent run.
How PRESHos identifies people and agents, decides what each may do, isolates the work and keeps the record. Written for the person reviewing it.
Identity, policy and evidenceacross agent execution.
Enterprise identity
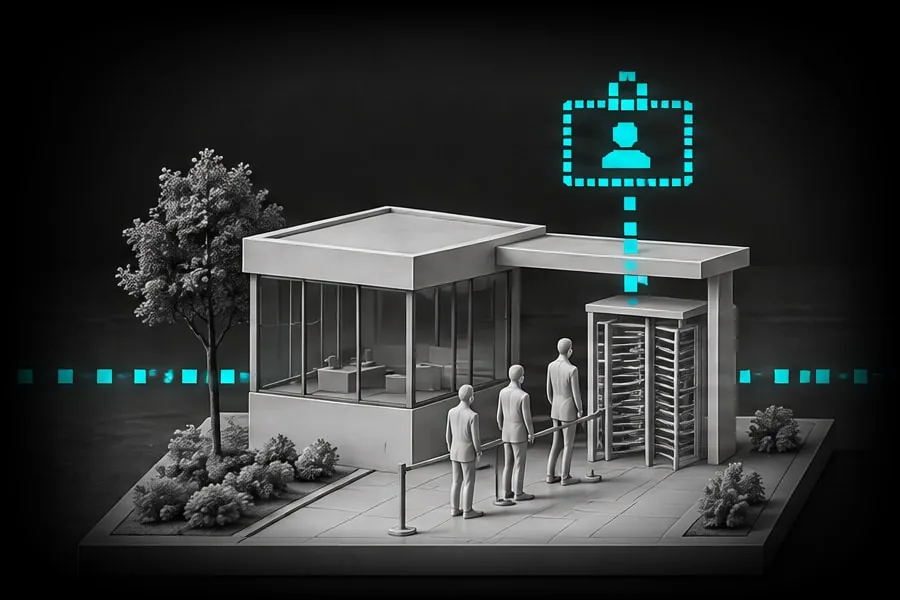
SSO and IdP integration
- MFA support, directory sync
- Active membership, session
Authorization
Tenant and membership bindingRBAC and tool policyUser contextRoles, ownership
Agent identityAssigned roles
Object, field and record scopes
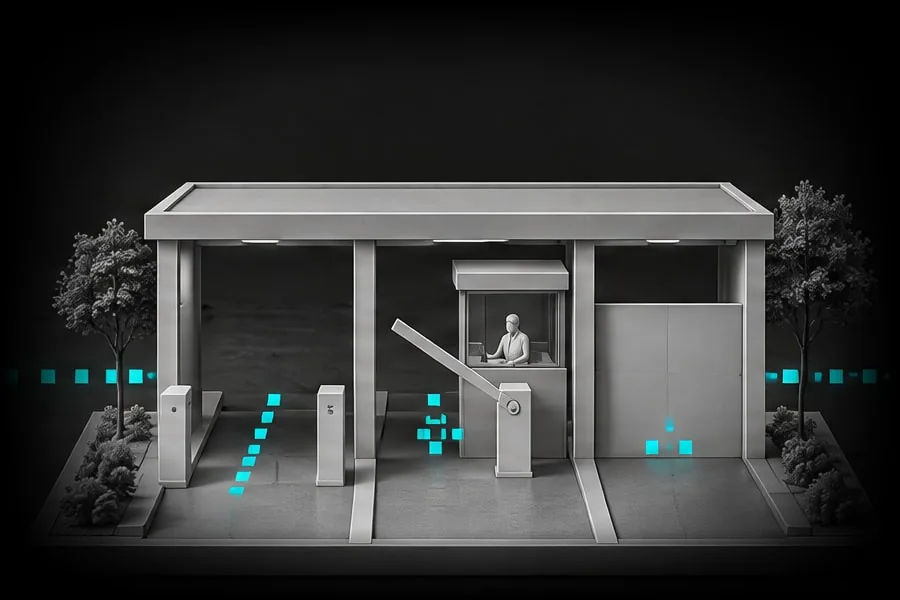
- Allow
- Approval
- Deny
Runtime choice
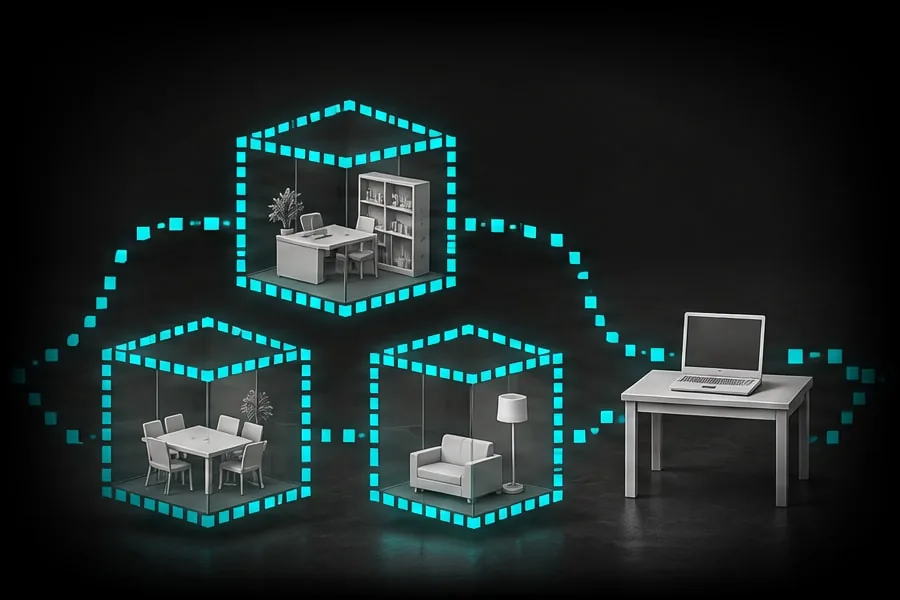
- Cloud
- Isolated session
- microVMs
- Local
- Enrolled Mac
- User workspace
Connected systems
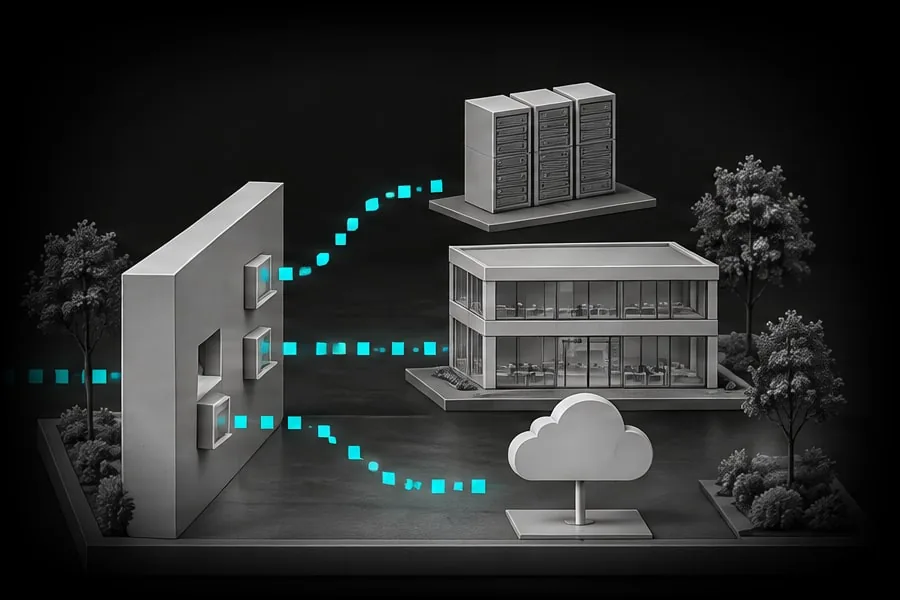
Configurable cloud egress
- SSRF safeguards
- Scoped access
- MCP, APIs and AI models
Shared security services
Protected data
- Encrypted storage
- Private file access
- Point-in-time recovery
Secrets vault
- Google Cloud Secret Manager
- Scoped runtime grants
- Server-side credentials
Audit and approvals
- Run and tool event traces
- Human approval records
- Actor, action, outcome
The detail,area by area.
What PRESHos enforces at each point of an agent run.
- SSO and identity provider integration
- MFA support
- Directory sync
- Tenant and membership binding
- Role-based access and tool policy
- Object, field and record scopes
- Each action is allowed, sent for approval or denied
- A personal agent acts as its owner, with the owner's access
- A team agent acts as itself, with its own assigned roles
- An agent never has more access than its owner
- Cloud sessions run in isolated microVMs
- Local sessions run on an enrolled Mac, in the user's workspace
- Configurable cloud egress
- SSRF safeguards
- Scoped access to MCP servers, APIs and AI models
- Encrypted storage
- Private file access
- Point-in-time recovery
- Google Cloud Secret Manager
- Scoped runtime grants
- Server-side credentials
- Run and tool event traces
- Human approval records
- Actor, action and outcome for each
Secrets stayin the vault.
Credentials are held in Google Cloud Secret Manager and granted to a run only for the scope it needs. They stay on the server.
How it fitsyour environment.
Your identity provider
SSO and identity provider integration, with MFA support and directory sync.
Runtime choice
Cloud sessions run in isolated microVMs. Local sessions run on an enrolled Mac, in the user's workspace.
Your infrastructure
For custom enterprise deployments, your data can be hosted in your own infrastructure.
Relatedreading.
More on Platform
AI & Automation
AI Works on a Copy: Approval Before Anything Reaches a Live System
Agents can do real work on a working copy of your data while a person approves what goes back. Here is how a digital twin and an approval gate work together.
AI Engineering
Choosing a Model per Agent: Match the Model to the Job
Different agent jobs suit different AI models. Here is how to choose a model per agent, compare options fairly and keep your controls the same throughout.
AI Engineering
Field-Level Permissions for Agents: Control Down to the Field
Field-level permissions decide which parts of a record an agent can read or change. Here is how roles, scopes and fields combine, with a worked example.
Reviewing PRESHos?
Bring us your security questions. We will walk through identity, authorization, runtime and the record with your team.